Essential Eight Explained: A Guide for Australian Businesses
Cyber security is no longer something Australian businesses can treat as an occasional IT task. Businesses of all sizes now depend on cloud applications, email, connected devices, online banking, customer databases and remote access. If one of these systems is poorly protected, a cyber incident can interrupt operations, expose information or create significant recovery costs.
For many businesses, knowing where to start can be difficult. There are countless security products, technical recommendations and compliance considerations, and not every business has a dedicated cyber security team.
The Essential Eight provides a practical starting point.
Developed by the Australian Signals Directorate (ASD), the Essential Eight brings together eight mitigation strategies designed to reduce the likelihood and impact of common cyber security incidents. The framework covers areas such as application control, patching, multi-factor authentication, administrative privileges and backups.
The framework is not a guarantee against every cyber threat. Instead, it provides a structured baseline that businesses can use to identify weaknesses, improve security controls and plan further improvements.
This article explains what the Essential Eight means for Australian businesses, what each strategy involves, how maturity levels work and what practical steps a business can take to start improving its security posture.
What Is the Essential Eight?
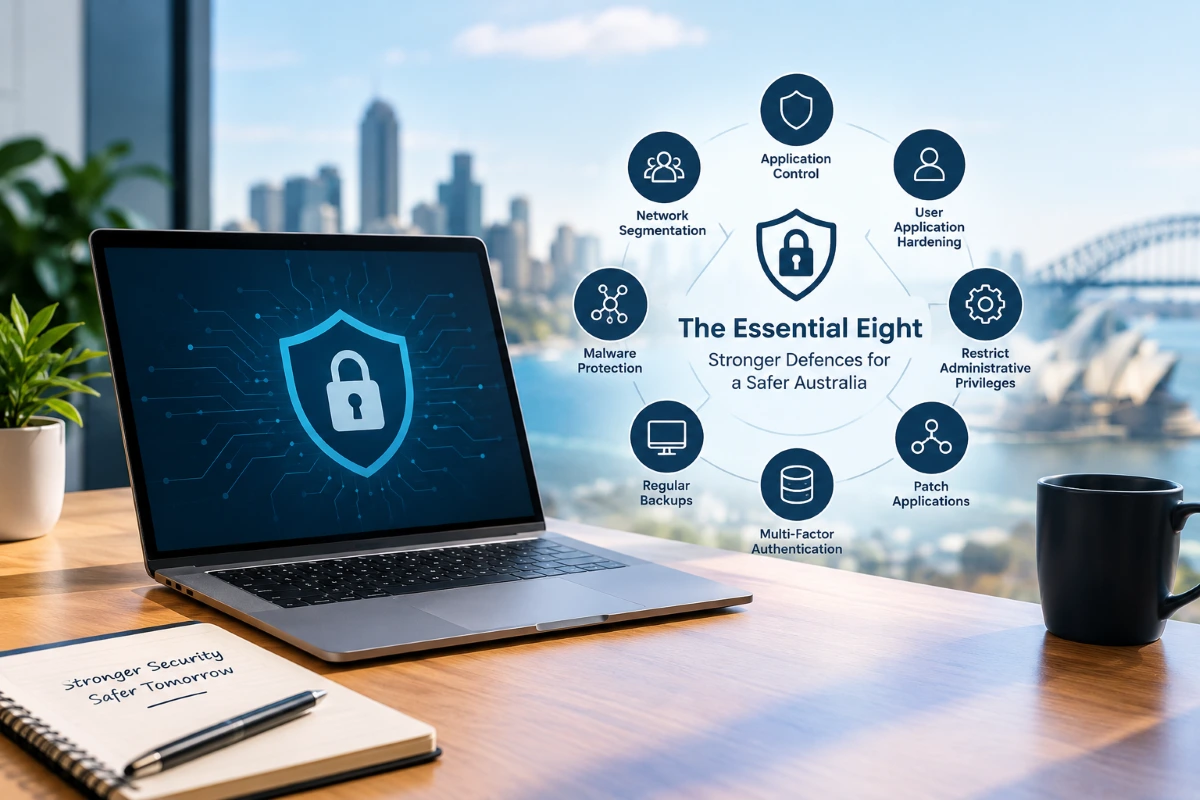
The Essential Eight is a set of eight cyber security mitigation strategies developed by the Australian Signals Directorate to help organisations reduce their exposure to common cyber threats.
The eight strategies are:
- Application control
- Patching applications
- Configuring Microsoft Office macros
- User application hardening
- Restricting administrative privileges
- Patching operating systems
- Multi-factor authentication
- Regular backups
The strategies work together rather than operating as eight separate security products.
For example, patching helps close known software vulnerabilities, while application control can limit which software is allowed to run. MFA adds protection to user accounts, while restricted administrative privileges can limit what a compromised account can change.
The ACSC describes the framework as a baseline for reducing cyber security incidents, while the maturity model provides more detailed requirements for implementation.
This makes the framework useful for businesses that want to move from general cyber security awareness towards a more structured approach.
Why Does the Essential Eight Matter for Australian Businesses?
Australian businesses face a range of cyber threats, including phishing, credential theft, ransomware, malicious software and exploitation of unpatched systems.
A business may have antivirus software installed and still have major security gaps. For example, an employee account could lack MFA, a server could be running outdated software, or an administrator account could have unnecessary access to critical systems.
The Essential Eight encourages businesses to address several of these areas together.
A structured approach can help businesses:
- Reduce exposure to common vulnerabilities
- Strengthen user account security
- Limit unauthorised software
- Reduce the impact of compromised accounts
- Improve protection against ransomware
- Establish more reliable backup practices
- Create a clearer cyber security improvement plan
- Measure progress through maturity levels
The ACSC also provides resources specifically for small businesses and recommends Maturity Level One as a starting point for small businesses.
That does not mean every organisation should stop at Level One. Businesses with more complex systems, higher security requirements or specific regulatory obligations may need stronger controls.
The Eight Essential Eight Strategies Explained
Understanding the names of the eight strategies is only the first step. The real value comes from understanding what they mean in day-to-day business operations.
1. Application Control
Application control determines which software is allowed to run on business systems.
Without appropriate controls, users may install applications without approval. Some software may be unnecessary, outdated or unsafe. Malicious software can also attempt to execute on a device after a phishing attack or other compromise.
Application control helps businesses create an approved software environment.
A practical implementation may involve:
- Maintaining an approved application list
- Blocking unauthorised executable files
- Controlling applications running from user and temporary folders
- Reviewing application control rules regularly
- Recording blocked or allowed events where required
The ACSC maturity model contains progressively stronger requirements for application control as organisations move through the maturity levels.
For a small business, this does not necessarily mean every employee needs a complicated security system. The important point is to understand what software should be running and prevent unnecessary applications from creating additional risk.
2. Patch Applications
Software vulnerabilities can provide attackers with opportunities to gain access to systems.
Applications such as web browsers, email clients, PDF software and productivity tools are commonly used across business environments. Keeping them updated helps address known vulnerabilities.
A proper patching process should identify:
- Which applications are installed
- Which versions are running
- Which devices need updates
- Which vulnerabilities require urgent attention
- Whether unsupported applications should be removed
The ACSC maturity model sets specific expectations around vulnerability scanning and patching timeframes at different maturity levels. For example, higher maturity levels introduce additional patching requirements and tighter timeframes for certain critical vulnerabilities.
Manual patching can become difficult when a business has dozens or hundreds of devices. Automated patch management and centralised monitoring can make the process more consistent.
3. Configure Microsoft Office Macros
Microsoft Office files can contain macros that automate tasks. While macros can have legitimate business uses, malicious documents can also use them to execute harmful activity.
The framework therefore includes controls around Microsoft Office macros.
Businesses should consider:
- Whether macros are genuinely required
- Which users have a legitimate business need for them
- Whether macros from internet-sourced documents should be blocked
- Whether security settings prevent users from weakening controls
- Whether antivirus scanning is enabled for macros
The ACSC maturity model includes progressively stronger requirements for controlling Microsoft Office macros.
This is particularly relevant where employees regularly receive documents through email or download files from external sources.
Security controls should still be supported by staff awareness. Employees should know that an unexpected document asking them to enable macros deserves careful attention.
4. User Application Hardening
Web browsers and other applications can provide another route for attackers if they are not configured securely.
User application hardening focuses on reducing unnecessary functionality and limiting risky behaviour within applications.
Depending on the environment, this can involve:
- Restricting unsafe browser features
- Preventing users from changing important security settings
- Blocking unnecessary content or functionality
- Keeping browsers and related software patched
- Removing outdated applications and browser components
The purpose is not to make everyday work difficult. Instead, it is to reduce the number of unnecessary features that an attacker could potentially exploit.
The ACSC maturity model provides specific technical requirements for application hardening at different levels.
Businesses should review these settings alongside their normal applications and workflows so that security controls remain practical for staff.
5. Restrict Administrative Privileges
Not every employee needs administrator access.
Giving users more privileges than necessary can increase the impact of a compromised account. If an attacker obtains an account with extensive administrative rights, they may have greater opportunities to modify systems, install software or access sensitive resources.
Restricting administrative privileges means users should receive only the access required to perform their roles.
For example:
- A finance employee may need accounting software but not server administration rights.
- A receptionist may need email and business applications but not permission to install system software.
- An external contractor may need temporary access to a specific system rather than unrestricted network access.
Access should also be reviewed when employees change roles or leave the organisation.
The ACSC notes that compromised privileged accounts can provide attackers with opportunities to gain further access and potentially affect data, including backups.
This is why access control should be treated as an ongoing process rather than something configured once.
6. Patch Operating Systems
Operating systems sit underneath many of the applications businesses rely on every day.
Windows, macOS, Linux and other operating systems receive security updates to address vulnerabilities and improve protection. Delaying important updates can leave devices exposed to known security weaknesses.
A business should maintain visibility over:
- Which operating systems are in use
- Which versions are installed
- Which devices are supported
- Whether security updates are being applied
- Which devices are approaching end of support
This is one area where accurate IT asset information becomes particularly useful.
If a business does not know which devices it owns or which operating systems they are running, it becomes much harder to maintain consistent patching.
For businesses managing multiple computers, centralised device management can help identify missing updates and provide better visibility across the environment.
7. Multi-Factor Authentication
Passwords alone do not provide enough protection for many modern business accounts.
Passwords can be stolen through phishing, credential reuse, malware or other techniques. Multi-factor authentication adds another verification step before access is granted.
Depending on the system, MFA may require something such as:
- A password or passphrase
- An authentication application
- A hardware security device
- Another approved authentication factor
The ACSC identifies MFA as one of the eight core mitigation strategies and provides specific implementation guidance within the maturity model.
Businesses should consider MFA for important online services, particularly accounts that provide access to sensitive information or administrative functions.
Microsoft 365, cloud platforms, remote access systems and other business applications should all be reviewed as part of an MFA assessment.
MFA is not a substitute for other controls. A business still needs secure devices, appropriate permissions, patching and monitoring.
8. Regular Backups
Backups are an important part of recovering from ransomware, accidental deletion, hardware failure and other incidents.
However, simply having a backup does not automatically mean a business can recover successfully.
A reliable backup strategy should consider:
- What data needs to be backed up
- How frequently backups should run
- Where backups are stored
- How long backups should be retained
- Who can access or modify them
- Whether backups are protected from unauthorised deletion
- Whether restoration has actually been tested
The ACSC maturity model states that backups should be performed and retained according to business criticality and continuity requirements, with restoration testing forming part of disaster recovery exercises.
This is why businesses should not judge backup protection solely by whether yesterday’s backup completed successfully.
The more important question is whether the business can restore its critical information when it needs it.
Businesses that want to review their current approach can also consider professional data backup and recovery services as part of a broader recovery strategy.
Understanding Essential Eight Maturity Levels
The Essential Eight does not simply ask whether a business has implemented each strategy. The maturity model provides different levels of implementation.
The framework includes Maturity Levels One, Two and Three, with higher levels introducing stronger and more comprehensive controls.
Maturity Level One
Level One provides a baseline approach and is particularly relevant to small businesses starting their cyber security improvement journey.
It establishes fundamental controls around patching, application control, MFA, administrative privileges, application hardening and backups.
Maturity Level Two
Level Two introduces stronger requirements and expands controls across the environment.
This can include more comprehensive application control, additional patching requirements, stronger privileged access restrictions and enhanced incident response expectations.
Maturity Level Three
Level Three provides more advanced controls for organisations requiring a stronger security posture.
Requirements become more comprehensive, including tighter controls around applications, privileged access, logging, patching and incident response.
Businesses should select an appropriate target based on their environment, risks, business requirements and security obligations rather than assuming the highest level is automatically necessary.
How Can a Business Start Implementing the Essential Eight?
Implementation should begin with understanding the current environment.
Trying to configure everything at once can create unnecessary disruption, especially for a business that has never completed a structured security assessment.
A practical starting process is:
- Create an accurate asset inventory
Identify computers, servers, mobile devices, network equipment, applications and important cloud services. - Review current security controls
Check MFA, administrator accounts, patching, backups, application controls and device security. - Identify gaps
Record where current systems do not meet the relevant requirements. - Prioritise the risks
Address controls that could create significant exposure or affect critical business systems. - Set a realistic target maturity level
Consider business size, industry, technology environment and risk profile. - Implement the controls
Make changes in a controlled way and document what has been completed. - Test and monitor
Security is an ongoing process. Controls need regular reviews to remain effective as systems and staff change.
A cybersecurity risk assessment can help businesses identify threats, vulnerabilities and existing controls before deciding which improvements should receive priority.
Does Every Australian Business Need the Same Approach?
No.
A small professional services business with ten employees and mostly cloud-based applications will have a different environment from a manufacturer operating servers, production systems and multiple locations.
The same framework can still provide a useful structure, but implementation should reflect the organisation.
Factors that may affect the approach include:
- Number of employees
- Number and type of devices
- Cloud services in use
- On-site servers
- Remote working arrangements
- Sensitive information handled
- Industry requirements
- Existing security controls
- Business continuity requirements
- Available internal IT resources
The ACSC provides resources for both small and larger organisations, and its small-business resources recommend starting with Maturity Level One.
The framework should therefore be used as a practical security baseline rather than a one-size-fits-all technology package.
Common Essential Eight Mistakes Businesses Make
Businesses can make progress with the framework and still leave important gaps if implementation becomes a box-ticking exercise.
Common problems include:
- Assuming antivirus software covers all eight strategies
- Enabling MFA but leaving unnecessary administrator accounts active
- Patching some devices while unknown devices remain unmanaged
- Creating backups without testing restoration
- Allowing users to install unapproved applications
- Treating the assessment as a one-off project
- Failing to review security when employees change roles
- Ignoring older systems that cannot easily receive updates
- Implementing controls without documenting exceptions
- Choosing security settings without considering how the business actually operates
The framework works best when security controls become part of normal IT management.
For example, patching should be part of regular device maintenance. Access reviews should happen when staff join, leave or change roles. Backup testing should be included in business continuity planning.
Businesses looking for ongoing technical oversight can also consider Managed IT Services where security, monitoring, maintenance and support need to be managed as part of the wider IT environment.
How the Essential Eight Fits Into Broader Cyber Security
The Essential Eight is an important baseline, but it is not the entire cyber security picture.
Businesses may also need to consider:
- Email security
- Network security
- Endpoint protection
- Security awareness training
- Incident response
- Vulnerability management
- Cloud security
- Data protection
- Mobile device security
- Business continuity
- Disaster recovery
- Security monitoring
The ACSC itself describes the Essential Eight as a baseline and provides additional mitigation strategies beyond the eight core controls.
For example, a business may implement MFA successfully but still have a poorly configured firewall. Another organisation may have strong endpoint protection but no tested backup recovery process.
A broader cyber security strategy for Australian businesses can therefore help put the eight controls into context.
Is the Essential Eight Still Relevant in 2026?
Yes, the framework remains an active Australian cyber security framework, although the broader guidance continues to evolve.
In June 2026, the Australian Signals Directorate announced consultation on the future evolution of the Essential Eight and proposed an expanded Essentials series intended to provide more flexibility while maintaining a clear path towards stronger cyber resilience. ASD stated that organisations already using the Essential Eight could expect strong alignment between existing controls and the proposed evolution.
This is important for businesses planning longer-term security improvements.
The goal should not be to implement a framework once and forget about it. Businesses should review official guidance periodically and adjust their controls as technology, threats and business requirements change.
What Should a Business Review First?
If your business has never assessed its cyber security against the framework, start with visibility.
Ask:
- Do we know every device connected to our business environment?
- Are important applications regularly patched?
- Are operating systems supported and updated?
- Is MFA enabled on important online services?
- Does every employee really need their current privileges?
- Can unauthorised applications run on business devices?
- Are Microsoft Office macro settings appropriately controlled?
- Are browsers and user applications securely configured?
- Are critical files backed up?
- Have backups actually been restored and tested?
- Do we have a process for responding to a cyber incident?
The answers will not provide a complete security assessment, but they can reveal where further investigation is needed.
Businesses can also review their broader IT security solutions to understand how security controls, monitoring and backup services can work together.
Frequently Asked Questions
1). What is the Essential Eight?
The Essential Eight is an Australian cyber security framework developed by the Australian Signals Directorate. It contains eight mitigation strategies covering areas such as patching, MFA, application control, privileged access and backups.
2). Is the Essential Eight mandatory for Australian businesses?
Not for every Australian business. It is an ASD-developed cyber security framework and may be relevant to organisations with specific contractual, regulatory or security requirements.
3). What are the eight Essential Eight controls?
They cover application control, application patching, Office macro controls, user application hardening, restricting administrative privileges, operating system patching, MFA and regular backups.
4). Which Essential Eight maturity level should a small business use?
The ACSC recommends Maturity Level One as a starting point for small businesses. The appropriate target can vary according to the organisation’s systems, risks and requirements.
5). Does the Essential Eight guarantee protection from cyber attacks?
No. The framework provides a baseline of mitigation strategies, but no set of controls can guarantee protection against every cyber threat.
Final Thoughts
The Essential Eight gives Australian businesses a structured way to review some of the most important areas of cyber security without trying to solve every security problem at once.
The real benefit comes from putting the controls into everyday IT operations. Devices need regular updates, user privileges need review, MFA needs consistent enforcement, applications need appropriate controls and backups need to be tested rather than simply assumed to work.
Businesses should also recognise that cyber security is an ongoing process. Staff change, applications are replaced, cloud services are added and new vulnerabilities emerge. A security setup that was appropriate two years ago may no longer provide the same level of protection today.
If you want to review where your business currently stands and identify practical improvements, IT Support Guy can help assess your technology environment and support ongoing security, maintenance and IT management.